Coinbase Says 99% of Customer Assets in Cold Storage After $6.3B Binance Hack
Key Takeaways
- Coinbase says more than 99% of customer assets are stored offline.
- Binance’s $6.34 billion theft prompted Coinbase to explain its custody defenses.
- Coinbase reported $377 billion in platform assets as of Sept. 30, 2026.
Coinbase Details Cold Storage Defenses After Binance Hack
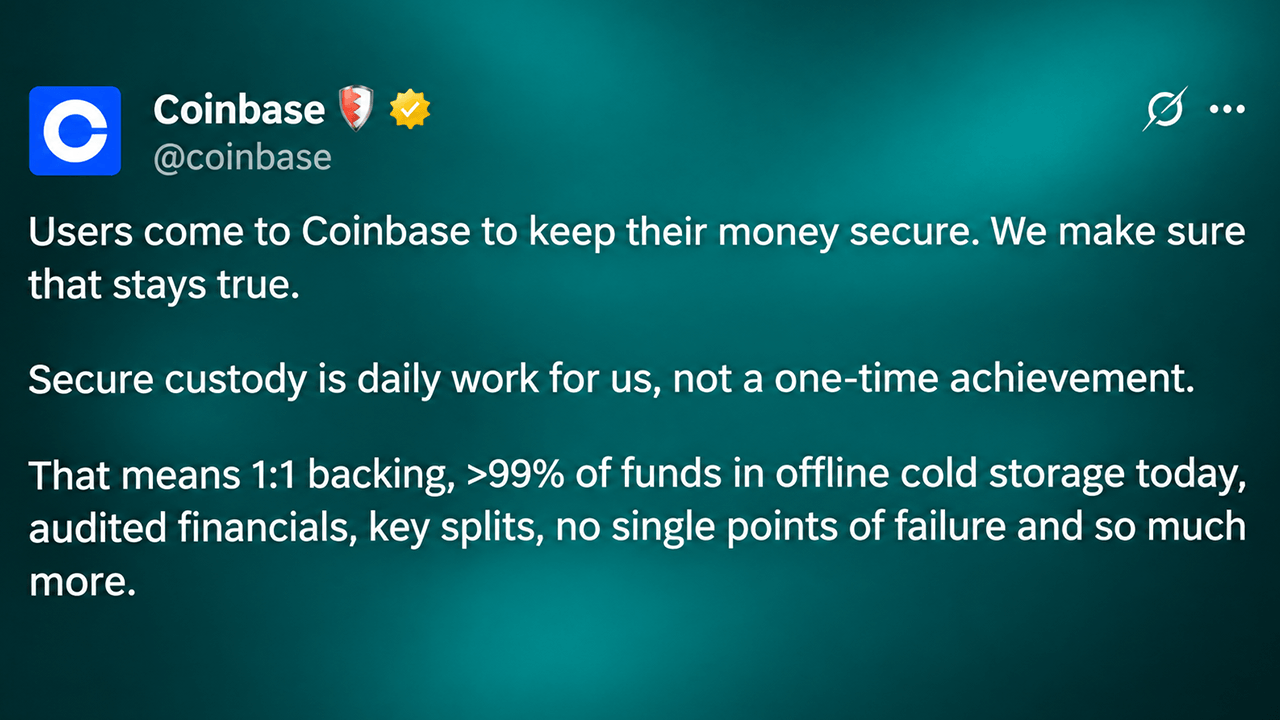
Coinbase said on Nov. 4, 2026, that more than 99% of customer assets are held in offline cold storage, outlining its security protections. The U.S.-based cryptocurrency exchange issued its statement on X, emphasizing the importance of maintaining customer confidence following the multibillion-dollar security breach at Binance, one of the world’s largest cryptocurrency trading platforms.
“Users come to Coinbase to keep their money secure. We make sure that stays true,” the U.S. exchange wrote.
The company continued:
“Secure custody is daily work for us, not a one-time achievement.”
In an accompanying blog post titled “How Coinbase Protects Customer Assets,” the exchange explained that its internet-connected hot wallets maintain sufficient liquidity for withdrawals and transfers, while excess balances are routinely shifted into offline custody.
Its institutional custody vault product operates entirely through cold storage, with holdings segregated onchain. Coinbase maintains that customer deposits are backed 1:1, remain customer property, and are never lent or deployed without authorization. The company said its infrastructure and customer funds were unaffected by the Binance incident.
How Does Coinbase Keep Customer Funds Safe?
Coinbase’s custody security relies on distributed cryptographic keys, transaction restrictions, and emergency controls intended to prevent unauthorized asset movements.
In the centralized exchange (CEX) platform’s cold-wallet operations, private keys are divided into separate components and never reconstructed in their entirety, even during transaction signing. Hot-wallet infrastructure, Coinbase says, requires multiple employees to authorize production changes, preventing any single individual from independently modifying critical signing services.
The exchange also employs automated anomaly detection and transfer limits that can interrupt suspicious withdrawals while security personnel investigate. Another safeguard involves emergency kill switches capable of disabling signing operations altogether. Coinbase explains that compromised systems cannot resume processing transactions until investigators determine that operations are secure.
Employee permissions are restricted through temporary access privileges, phishing-resistant authentication, and additional approval requirements for sensitive activities. These arrangements are intended to limit the damage caused by stolen credentials, compromised devices or malicious insiders.
However, Coinbase’s claim that more than 99% of customer assets are stored offline is self-reported, and the precise allocation has not been independently established by third parties.
What Did the $6.34 Billion Binance Hack Expose?
The Oct. 29 Binance attack involved a sophisticated social engineering campaign that compromised employee devices and eventually reached Binance’s internal wallet-signing infrastructure. Attackers drained approximately $6.34 billion in cryptocurrencies across multiple blockchain networks, Binance said, making it the largest reported cryptocurrency exchange theft to date.
Binance temporarily suspended withdrawals while coordinating with stablecoin issuers and other industry participants to freeze or intercept stolen assets. The exchange subsequently pledged to cover affected customer balances through corporate reserves and its Secure Asset Fund for Users (SAFU).
For perspective, the February 2025 Bybit breach resulted in approximately $1.5 billion in stolen cryptocurrencies—then a record for the industry, but substantially less than the losses attributed to last week’s Binance incident. The record-setting Binance theft has intensified scrutiny of online custody systems, particularly the operational procedures governing access to private keys and authorization of large transactions.
Is Coinbase Safe After the Binance Hack?
Coinbase points to its financial disclosures, regulatory supervision, and independent control examinations as supporting evidence of its custody practices. As of Sept. 30, 2026, the company reported $8.6 billion in cash and cash equivalents, $2.2 billion in crypto assets held for investment, and $377 billion in total assets on its platform.
The exchange is publicly traded in the United States, files audited annual financial statements with the Securities and Exchange Commission (SEC), and operates under numerous regulatory licenses. Its U.S. custody subsidiary, Coinbase Custody Trust Company, is regulated by the New York Department of Financial Services (NYDFS).
The company has also completed SOC 1 Type II and SOC 2 Type II examinations covering specified operational controls. Those examinations provide assurance about the controls within their assessed scope, but they do not independently establish that every customer asset is protected against theft. Coinbase further acknowledged that advances in artificial intelligence (AI) are changing cybersecurity threats, requiring continued investment in defensive technology.
Ultimately, the company’s disclosed safeguards explain how it seeks to protect customer holdings, but its cold-storage percentage remains a company-reported figure rather than an independently verified guarantee against future attacks.